

Descripción
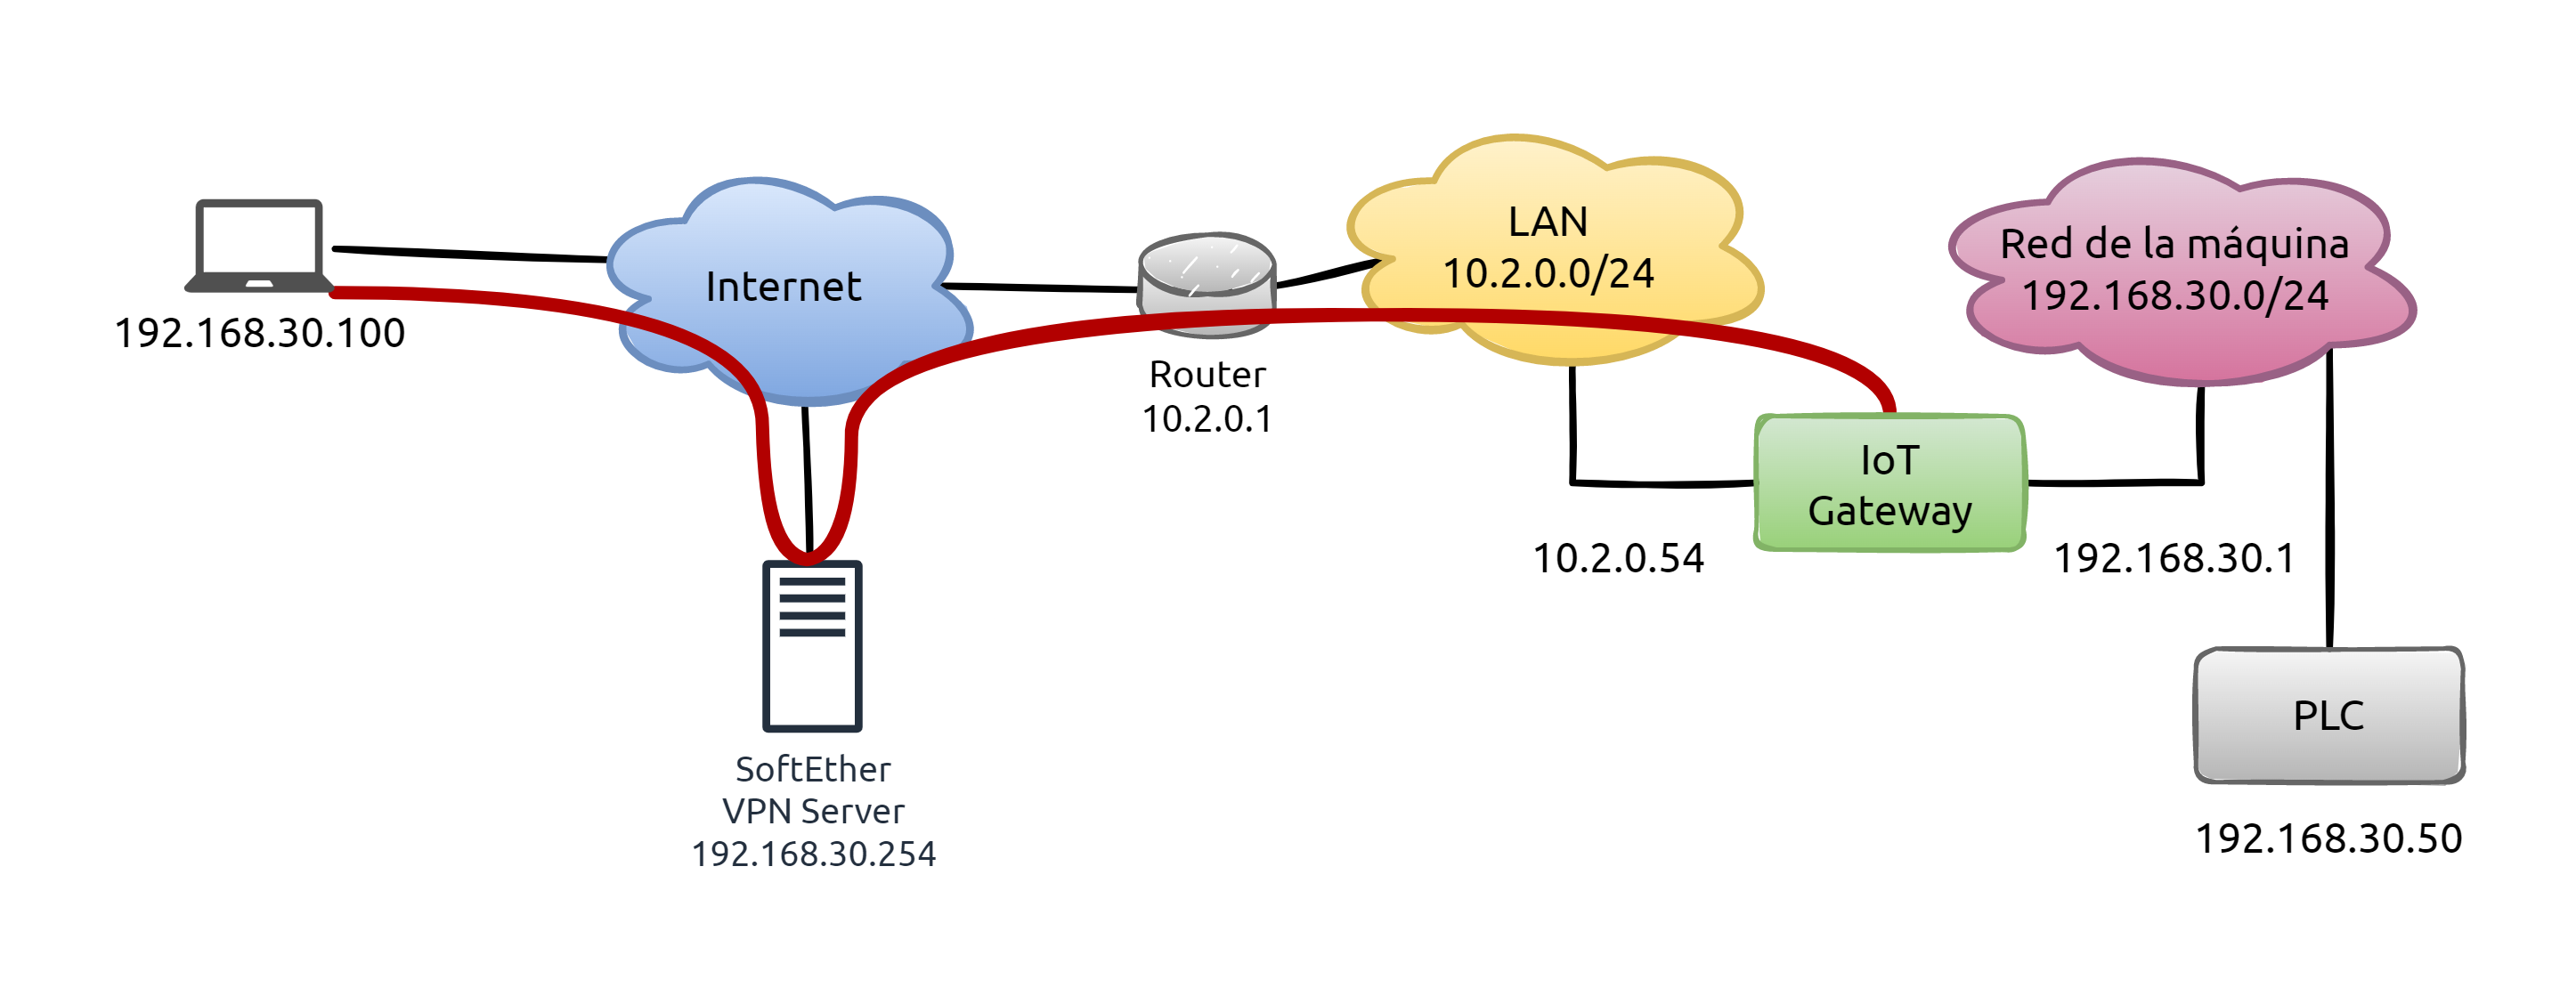
Suponemos que la empresa tiene una red con acceso a Internet y que nos asigna IP por DHCP. Colocaremos nuestro IoT GW con su interface WAN conectada a esta red y la interface LAN del IoT GW la conectaremos a la red donde tenemos el PLC que conecta a la máquina, típicamente al Switch IP de la máquina.
En el IoT GW instalamos SoftEther para permitir acceso vía VPN a la red de la máquina. De esta forma el portátil del técnico (192.168.30.100) podrá acceder a los equipos de la máquina con un acceso de capa 2.
No podemos esperar que en el router de la empresa nos abran ningún puerto para facilitar esta comunicación. Por este motivo usamos un tercer servidor en Internet al que llamamos SoftEther VPN Server que actuará como relay de la comunicación evitando la necesidad de abrir puertos.
Instalación SoftEther en Ubuntu 18.04
Este proceso hay que repetirlo dos veces. Una para el IoT Gateway y otra para el VPN server que instalaremos en el relay server.
sudo apt-get update && sudo apt-get upgrade -y && sudo apt-get autoremove -y
apt-get -y install build-essential wget curl gcc make wget tzdata git libreadline-dev libncurses-dev libssl-dev zlib1g-dev

wget https://github.com/SoftEtherVPN/SoftEtherVPN_Stable/releases/download/v4.39-9772-beta/softether-vpnserver-v4.39-9772-beta-2022.04.26-linux-x64-64bit.tar.gz
tar xzf softether-vpnserver-v4.39-9772-beta-2022.04.26-linux-x64-64bit.tar.gz && rm softether-vpnserver-v4.39-9772-beta-2022.04.26-linux-x64-64bit.tar.gz

cd vpnserver && sudo make
cd ..
sudo mv vpnserver /usr/local && cd /usr/local/vpnserver/
sudo chmod 600 *
sudo chmod 700 vpnserver vpncmd lib chain_certs

sudo cat >> /lib/systemd/system/vpnserver.service << EOF
[Unit]
Description=SoftEther VPN Server
After=network.target

[Service]
Type=forking
ExecStart=/usr/local/vpnserver/vpnserver start
ExecStop=/usr/local/vpnserver/vpnserver stop

[Install]
WantedBy=multi-user.target
EOF

echo net.ipv4.ip_forward = 1 | ${SUDO} tee -a /etc/sysctl.conf
echo net.ipv6.ip_forward = 1 | ${SUDO} tee -a /etc/sysctl.conf

sysctl -p

systemctl enable vpnserver
systemctl start vpnserver
systemctl stop vpnserver
systemctl restart vpnserver
systemctl status vpnserver
Ficheros de configuración
Cliente:
📎 fabrica.vpn 1.3KB
# VPN Client VPN Connection Setting File
#
# This file is exported using the VPN Client Manager.
# The contents of this file can be edited using a text editor.
#
# When this file is imported to the Client Connection Manager
#  it can be used immediately.

declare root
{
	bool CheckServerCert false
	uint64 CreateDateTime 0
	uint64 LastConnectDateTime 0
	bool StartupAccount false
	uint64 UpdateDateTime 0

	declare ClientAuth
	{
		uint AuthType 1
		byte HashedPassword Ol/gsD/yCXmUkHUzG47q0ygozDQ=
		string Username rai
	}
	declare ClientOption
	{
		string AccountName fabrica
		uint AdditionalConnectionInterval 1
		uint ConnectionDisconnectSpan 0
		string DeviceName VPN
		bool DisableQoS false
		bool HalfConnection false
		bool HideNicInfoWindow false
		bool HideStatusWindow false
		string Hostname i40sys-video.softether.net
		string HubName VPN
		uint MaxConnection 1
		bool NoRoutingTracking false
		bool NoTls1 false
		bool NoUdpAcceleration false
		uint NumRetry 4294967295
		uint Port 443
		uint PortUDP 0
		string ProxyName $
		byte ProxyPassword $
		uint ProxyPort 0
		uint ProxyType 0
		string ProxyUsername $
		bool RequireBridgeRoutingMode false
		bool RequireMonitorMode false
		uint RetryInterval 15
		bool UseCompress false
		bool UseEncrypt true
	}
}
Gateway IOT
📎 vpn_server.config 15.2KB
# Software Configuration File
# ---------------------------
#
# You may edit this file when the VPN Server / Client / Bridge program is not running.
#
# In prior to edit this file manually by your text editor,
# shutdown the VPN Server / Client / Bridge background service.
# Otherwise, all changes will be lost.
#
declare root
{
	uint ConfigRevision 14
	bool IPsecMessageDisplayed true
	string Region ES
	bool VgsMessageDisplayed false

	declare DDnsClient
	{
		bool Disabled false
		byte Key y3vwwtbYbiGzAKrCKJ4HAIEWp7M=
		string LocalHostname iot-gw
		string ProxyHostName $
		uint ProxyPort 0
		uint ProxyType 0
		string ProxyUsername $
	}
	declare IPsec
	{
		bool EtherIP_IPsec false
		string IPsec_Secret vpn
		string L2TP_DefaultHub RedMaquina
		bool L2TP_IPsec false
		bool L2TP_Raw false

		declare EtherIP_IDSettingsList
		{
		}
	}
	declare ListenerList
	{
		declare Listener0
		{
			bool DisableDos false
			bool Enabled true
			uint Port 443
		}
		declare Listener1
		{
			bool DisableDos false
			bool Enabled true
			uint Port 992
		}
		declare Listener2
		{
			bool DisableDos false
			bool Enabled true
			uint Port 1194
		}
		declare Listener3
		{
			bool DisableDos false
			bool Enabled true
			uint Port 5555
		}
	}
	declare LocalBridgeList
	{
		bool DoNotDisableOffloading false

		declare LocalBridge0
		{
			string DeviceName ens3
			string HubName RedMaquina
			bool LimitBroadcast false
			bool MonitorMode false
			bool NoPromiscuousMode false
			bool TapMode false
		}
	}
	declare ServerConfiguration
	{
		bool AcceptOnlyTls true
		uint64 AutoDeleteCheckDiskFreeSpaceMin 104857600
		uint AutoDeleteCheckIntervalSecs 300
		uint AutoSaveConfigSpan 300
		bool BackupConfigOnlyWhenModified true
		string CipherName AES128-SHA
		uint CurrentBuild 9772
		bool DisableCoreDumpOnUnix false
		bool DisableDeadLockCheck false
		bool DisableDosProction false
		bool DisableGetHostNameWhenAcceptTcp false
		bool DisableIntelAesAcceleration false
		bool DisableIPsecAggressiveMode false
		bool DisableIPv6Listener false
		bool DisableJsonRpcWebApi false
		bool DisableNatTraversal false
		bool DisableOpenVPNServer false
		bool DisableSessionReconnect false
		bool DisableSSTPServer false
		bool DontBackupConfig false
		bool EnableVpnAzure false
		bool EnableVpnOverDns false
		bool EnableVpnOverIcmp false
		byte HashedPassword aIJuKtiiV5Bm//70tFb60QlvT+Y=
		string KeepConnectHost keepalive.softether.org
		uint KeepConnectInterval 50
		uint KeepConnectPort 80
		uint KeepConnectProtocol 1
		uint64 LoggerMaxLogSize 1073741823
		uint MaxConcurrentDnsClientThreads 512
		uint MaxConnectionsPerIP 256
		uint MaxUnestablishedConnections 1000
		bool NoHighPriorityProcess false
		bool NoLinuxArpFilter false
		bool NoSendSignature false
		string OpenVPNDefaultClientOption dev-type$20tun,link-mtu$201500,tun-mtu$201500,cipher$20AES-128-CBC,auth$20SHA1,keysize$20128,key-method$202,tls-client
		string OpenVPN_UdpPortList 1194
		bool SaveDebugLog false
		byte ServerCert MIIDgjCCAmqgAwIBAgIBADANBgkqhkiG9w0BAQsFADBAMQ8wDQYDVQQDDAZpb3QtZ3cxDzANBgNVBAoMBmlvdC1ndzEPMA0GA1UECwwGaW90LWd3MQswCQYDVQQGEwJVUzAeFw0yMjA2MDkwNTE4MDFaFw0zNzEyMzEwNTE4MDFaMEAxDzANBgNVBAMMBmlvdC1ndzEPMA0GA1UECgwGaW90LWd3MQ8wDQYDVQQLDAZpb3QtZ3cxCzAJBgNVBAYTAlVTMIIBIjANBgkqhkiG9w0BAQEFAAOCAQ8AMIIBCgKCAQEAtIQtJjaUFGRXsL4SlV3V9cMoXI45voRrPcKUXUQYbrrD6cUHDfrgS+OqOUnVyF8+CE5t3bKmcRuM2nWWveqvLlvXwwHVrZeV46MDJzU341YTDL0EvJWu5x6fxJc/98LSSVAVPyrbw3b6wncsp/FxN8+pDnXWHhPqrzHolW7LCjUTQj60VN+Tp4/46BG66Q/4LfzgaZ5vFhc3hWPzV3fRJ1umYrCMPO1yk52puvsmKmVCgnZifVuEiBwzEoWkykz7OdWun/pbejbcs99VqvR1vlxpkFtBUnajaAelVfdwVwWsBkgRnDJyMQbY4Ky6/fvsMDLLxDPUjuf9a8Eqz/INewIDAQABo4GGMIGDMA8GA1UdEwEB/wQFMAMBAf8wCwYDVR0PBAQDAgH2MGMGA1UdJQRcMFoGCCsGAQUFBwMBBggrBgEFBQcDAgYIKwYBBQUHAwMGCCsGAQUFBwMEBggrBgEFBQcDBQYIKwYBBQUHAwYGCCsGAQUFBwMHBggrBgEFBQcDCAYIKwYBBQUHAwkwDQYJKoZIhvcNAQELBQADggEBAHeWKJAc7lDvXYq0TS0FTdQhNTJkEKuncMTNL1b6FHlhVvDoz7VrzP+M/odwEnZipdvjhgiotW9NRTagMWQpRzGqFuZAouAlMgzX16wjzrvopIWzJj7CgKto3MgdkQLW48/bte05RM9rZCSkfJWRafLeXRb6P0xh+zKO3wq3xk4jUoPbOur3hNwoS5sfPgNRoMt0UJH/YLw9GqqbwMnj3mU6V9uP0emBiHPu3EUqjmQv3m/yeSi0or/gtdcr3nCvAgFq+kr5lS9VPdr9GZxzux2dUjRtNwYI4hbB2xApm16M6eZzWYEzM4zc419cWaw3HLFXB4+tc3LFpC7co86yPjU=
		byte ServerKey MIIEpAIBAAKCAQEAtIQtJjaUFGRXsL4SlV3V9cMoXI45voRrPcKUXUQYbrrD6cUHDfrgS+OqOUnVyF8+CE5t3bKmcRuM2nWWveqvLlvXwwHVrZeV46MDJzU341YTDL0EvJWu5x6fxJc/98LSSVAVPyrbw3b6wncsp/FxN8+pDnXWHhPqrzHolW7LCjUTQj60VN+Tp4/46BG66Q/4LfzgaZ5vFhc3hWPzV3fRJ1umYrCMPO1yk52puvsmKmVCgnZifVuEiBwzEoWkykz7OdWun/pbejbcs99VqvR1vlxpkFtBUnajaAelVfdwVwWsBkgRnDJyMQbY4Ky6/fvsMDLLxDPUjuf9a8Eqz/INewIDAQABAoIBAANTch+DnuvXQ3RatC3zWidajqpR5od3miA7rw8e25Jit4xdmHkt96b+TVsb3KgB9Tsi8sxEZ+OqnchCpWHfapXglFOf+4dkxRq6HKtCxEJYiiZQbz9oRJ42hrwRC1ktykEWjCWrTPxHe2xM1NJNVQgxt8wv6J+KP2c19LKYJX6NHt1e0VEp+9IlBmVAhtRJQ40ulFahL+LOKbyVUyKeFtEwPavlMgAID+LI6aBOFtghXj68xgSWRc7D4PVFgQFxYN5tsxo/WlTSNplLVACsDr1g99nhgytIaVjruvDVDuNAnU1C8RBK1jwTTKEgIX5QWpjkEJF2hEMehVcjLACNLmkCgYEA4H+T+cSLBQl0eZ4hgEUNdxJPB3e1aKTKdyVTTOPfILYwp9Qddn6Qqek1CNLNBGbeF3OKbquJ6ud02H8WoIVWmaYdHcxc1LoOS0KZdUDm37UgcdN55dT8E5JyHtaK/2Q+k/6o68weCRO1pHKNDbbv1cMUnibcOxfNwR/yx5g0wHMCgYEAzditVtFaY/oLsbAkk++SLKJh8bSibFBtmpXm8boKqFOvvcJwVnbL5MoKaOQAGC1GbROU+ZLKagYPZw1z1Yhn2HLYXEKBUAP93Y1GBpNhxaU6b1es3+7HtIwbVPsGUAVvGVP/wSpPcv3TpwldWJeJZ0Fo63ZQjjMzJ7Kgq5I6ZNkCgYEAhK8ieEaPm8SA0LiDOFqXoL5zcwhvcY+kElM/LnynjZ/glfCqETSwr5ujurlMbsOVk+q38Lz14J430xUZ/HmSO3GQV+JHI3tro1OTe1eGnMVijaPdsdb1vWOai1tl/5fx3Gpw0BxtzBOYEb+aWna6vW51KxvwogRpmTEWvpzY4L0CgYEArogMGLNzL5ef+K2/pcsYJk4cO4MLwEjFVa/J26UBSk2CkaNd+oHJSRhhkSPYTKd+shdLVfy3MQQoZRkL4L5CRkzB1B/zYnOv+PzCpeqqmJkKncM56bicjSHKPtiENq8UzuXg0Nhd+sLqhRM0mVwK/YiBPDvZ+2e/9OXIwxA+AKkCgYARy/SZMQeZ8HPeEEmepA8fY6ZmxhYWsQIgrEX+lkgiXaEIAFSi7KaZtPcjybi5ADob+Ao0CKXkTnfx32aDhl16l/AQeOIjxHf85VQrZp57UWTOD3HLI4RMjLJiWo+/ypUytduaS4Fo637liDVcfCQTjw6qpEhDM7UByeb4RJ4I+Q==
		uint ServerLogSwitchType 4
		uint ServerType 0
		bool StrictSyslogDatetimeFormat false
		bool Tls_Disable1_0 false
		bool Tls_Disable1_1 false
		bool Tls_Disable1_2 false
		bool Tls_Disable1_3 false
		bool UseKeepConnect true
		bool UseWebTimePage false
		bool UseWebUI false

		declare GlobalParams
		{
			uint FIFO_BUDGET 10240000
			uint HUB_ARP_SEND_INTERVAL 5000
			uint IP_TABLE_EXPIRE_TIME 60000
			uint IP_TABLE_EXPIRE_TIME_DHCP 300000
			uint MAC_TABLE_EXPIRE_TIME 600000
			uint MAX_BUFFERING_PACKET_SIZE 2560000
			uint MAX_HUB_LINKS 1024
			uint MAX_IP_TABLES 65536
			uint MAX_MAC_TABLES 65536
			uint MAX_SEND_SOCKET_QUEUE_NUM 128
			uint MAX_SEND_SOCKET_QUEUE_SIZE 2560000
			uint MAX_STORED_QUEUE_NUM 1024
			uint MEM_FIFO_REALLOC_MEM_SIZE 655360
			uint MIN_SEND_SOCKET_QUEUE_SIZE 320000
			uint QUEUE_BUDGET 2048
			uint SELECT_TIME 256
			uint SELECT_TIME_FOR_NAT 30
			uint STORM_CHECK_SPAN 500
			uint STORM_DISCARD_VALUE_END 1024
			uint STORM_DISCARD_VALUE_START 3
		}
		declare ServerTraffic
		{
			declare RecvTraffic
			{
				uint64 BroadcastBytes 26429925
				uint64 BroadcastCount 341356
				uint64 UnicastBytes 191562547
				uint64 UnicastCount 1940675
			}
			declare SendTraffic
			{
				uint64 BroadcastBytes 280189
				uint64 BroadcastCount 4041
				uint64 UnicastBytes 18125449
				uint64 UnicastCount 301616
			}
		}
		declare SyslogSettings
		{
			string HostName $
			uint Port 0
			uint SaveType 0
		}
	}
	declare VirtualHUB
	{
		declare RedMaquina
		{
			uint64 CreatedTime 1654805203240
			byte HashedPassword aIJuKtiiV5Bm//70tFb60QlvT+Y=
			uint64 LastCommTime 1654806766516
			uint64 LastLoginTime 1654805203239
			uint NumLogin 0
			bool Online true
			bool RadiusConvertAllMsChapv2AuthRequestToEap false
			string RadiusRealm $
			uint RadiusRetryInterval 0
			uint RadiusServerPort 1812
			string RadiusSuffixFilter $
			bool RadiusUsePeapInsteadOfEap false
			byte SecurePassword NBzwzV1sFkolfiVwR4lygwpxFpY=
			uint Type 0

			declare AccessList
			{
			}
			declare AdminOption
			{
				uint allow_hub_admin_change_option 0
				uint deny_bridge 0
				uint deny_change_user_password 0
				uint deny_empty_password 0
				uint deny_hub_admin_change_ext_option 0
				uint deny_qos 0
				uint deny_routing 0
				uint max_accesslists 0
				uint max_bitrates_download 0
				uint max_bitrates_upload 0
				uint max_groups 0
				uint max_multilogins_per_user 0
				uint max_sessions 0
				uint max_sessions_bridge 0
				uint max_sessions_client 0
				uint max_sessions_client_bridge_apply 0
				uint max_users 0
				uint no_access_list_include_file 0
				uint no_cascade 0
				uint no_change_access_control_list 0
				uint no_change_access_list 0
				uint no_change_admin_password 0
				uint no_change_cert_list 0
				uint no_change_crl_list 0
				uint no_change_groups 0
				uint no_change_log_config 0
				uint no_change_log_switch_type 0
				uint no_change_msg 0
				uint no_change_users 0
				uint no_delay_jitter_packet_loss 0
				uint no_delete_iptable 0
				uint no_delete_mactable 0
				uint no_disconnect_session 0
				uint no_enum_session 0
				uint no_offline 0
				uint no_online 0
				uint no_query_session 0
				uint no_read_log_file 0
				uint no_securenat 0
				uint no_securenat_enabledhcp 0
				uint no_securenat_enablenat 0
			}
			declare CascadeList
			{
				declare Cascade0
				{
					bool CheckServerCert false
					bool Online true

					declare ClientAuth
					{
						uint AuthType 1
						byte HashedPassword LVLDtHUZssdO/Gl9LFiDOq9kEks=
						string Username fabrica
					}
					declare ClientOption
					{
						string AccountName RelayServer
						uint AdditionalConnectionInterval 1
						uint ConnectionDisconnectSpan 0
						string DeviceName _SEHUBLINKCLI_
						bool DisableQoS false
						bool HalfConnection false
						bool HideNicInfoWindow false
						bool HideStatusWindow false
						string Hostname i40sys-video.softether.net
						string HubName VPN
						uint MaxConnection 8
						bool NoRoutingTracking true
						bool NoTls1 false
						bool NoUdpAcceleration false
						uint NumRetry 4294967295
						uint Port 443
						uint PortUDP 0
						string ProxyName $
						byte ProxyPassword $
						uint ProxyPort 0
						uint ProxyType 0
						string ProxyUsername $
						bool RequireBridgeRoutingMode true
						bool RequireMonitorMode false
						uint RetryInterval 10
						bool UseCompress false
						bool UseEncrypt true
					}
					declare Policy
					{
						bool ArpDhcpOnly false
						bool CheckIP false
						bool CheckIPv6 false
						bool CheckMac false
						bool DHCPFilter false
						bool DHCPForce false
						bool DHCPNoServer false
						bool DHCPv6Filter false
						bool DHCPv6NoServer false
						bool FilterIPv4 false
						bool FilterIPv6 false
						bool FilterNonIP false
						uint MaxDownload 0
						uint MaxIP 0
						uint MaxIPv6 0
						uint MaxMac 0
						uint MaxUpload 0
						bool NoBroadcastLimiter false
						bool NoIPv6DefaultRouterInRA false
						bool NoIPv6DefaultRouterInRAWhenIPv6 false
						bool NoServer false
						bool NoServerV6 false
						bool RAFilter false
						bool RSandRAFilter false
						uint VLanId 0
					}
				}
			}
			declare LogSetting
			{
				uint PacketLogSwitchType 4
				uint PACKET_LOG_ARP 0
				uint PACKET_LOG_DHCP 1
				uint PACKET_LOG_ETHERNET 0
				uint PACKET_LOG_ICMP 0
				uint PACKET_LOG_IP 0
				uint PACKET_LOG_TCP 0
				uint PACKET_LOG_TCP_CONN 1
				uint PACKET_LOG_UDP 0
				bool SavePacketLog true
				bool SaveSecurityLog true
				uint SecurityLogSwitchType 4
			}
			declare Message
			{
			}
			declare Option
			{
				uint AccessListIncludeFileCacheLifetime 30
				uint AdjustTcpMssValue 0
				bool ApplyIPv4AccessListOnArpPacket false
				bool AssignVLanIdByRadiusAttribute false
				bool BroadcastLimiterStrictMode false
				uint BroadcastStormDetectionThreshold 0
				uint ClientMinimumRequiredBuild 0
				bool DenyAllRadiusLoginWithNoVlanAssign false
				uint DetectDormantSessionInterval 0
				bool DisableAdjustTcpMss false
				bool DisableCheckMacOnLocalBridge false
				bool DisableCorrectIpOffloadChecksum false
				bool DisableHttpParsing false
				bool DisableIPParsing false
				bool DisableIpRawModeSecureNAT false
				bool DisableKernelModeSecureNAT false
				bool DisableUdpAcceleration false
				bool DisableUdpFilterForLocalBridgeNic false
				bool DisableUserModeSecureNAT false
				bool DoNotSaveHeavySecurityLogs false
				bool DropArpInPrivacyFilterMode true
				bool DropBroadcastsInPrivacyFilterMode true
				bool FilterBPDU false
				bool FilterIPv4 false
				bool FilterIPv6 false
				bool FilterNonIP false
				bool FilterOSPF false
				bool FilterPPPoE false
				uint FloodingSendQueueBufferQuota 33554432
				bool ManageOnlyLocalUnicastIPv6 true
				bool ManageOnlyPrivateIP true
				uint MaxLoggedPacketsPerMinute 0
				uint MaxSession 0
				bool NoArpPolling false
				bool NoDhcpPacketLogOutsideHub true
				bool NoEnum false
				bool NoIpTable false
				bool NoIPv4PacketLog false
				bool NoIPv6AddrPolling false
				bool NoIPv6DefaultRouterInRAWhenIPv6 true
				bool NoIPv6PacketLog false
				bool NoLookBPDUBridgeId false
				bool NoMacAddressLog true
				bool NoManageVlanId false
				bool NoPhysicalIPOnPacketLog false
				bool NoSpinLockForPacketDelay false
				bool RemoveDefGwOnDhcpForLocalhost true
				uint RequiredClientId 0
				uint SecureNAT_MaxDnsSessionsPerIp 0
				uint SecureNAT_MaxIcmpSessionsPerIp 0
				uint SecureNAT_MaxTcpSessionsPerIp 0
				uint SecureNAT_MaxTcpSynSentPerIp 0
				uint SecureNAT_MaxUdpSessionsPerIp 0
				bool SecureNAT_RandomizeAssignIp false
				bool SuppressClientUpdateNotification false
				bool UseHubNameAsDhcpUserClassOption false
				bool UseHubNameAsRadiusNasId false
				string VlanTypeId 0x8100
				bool YieldAfterStorePacket false
			}
			declare SecureNAT
			{
				bool Disabled true
				bool SaveLog true

				declare VirtualDhcpServer
				{
					string DhcpDnsServerAddress 192.168.30.1
					string DhcpDnsServerAddress2 0.0.0.0
					string DhcpDomainName $
					bool DhcpEnabled true
					uint DhcpExpireTimeSpan 7200
					string DhcpGatewayAddress 192.168.30.1
					string DhcpLeaseIPEnd 192.168.30.200
					string DhcpLeaseIPStart 192.168.30.10
					string DhcpPushRoutes $
					string DhcpSubnetMask 255.255.255.0
				}
				declare VirtualHost
				{
					string VirtualHostIp 192.168.30.1
					string VirtualHostIpSubnetMask 255.255.255.0
					string VirtualHostMacAddress 5E-BD-52-9D-F4-CC
				}
				declare VirtualRouter
				{
					bool NatEnabled true
					uint NatMtu 1500
					uint NatTcpTimeout 1800
					uint NatUdpTimeout 60
				}
			}
			declare SecurityAccountDatabase
			{
				declare CertList
				{
				}
				declare CrlList
				{
				}
				declare GroupList
				{
				}
				declare IPAccessControlList
				{
				}
				declare UserList
				{
				}
			}
			declare Traffic
			{
				declare RecvTraffic
				{
					uint64 BroadcastBytes 418882
					uint64 BroadcastCount 6269
					uint64 UnicastBytes 427183
					uint64 UnicastCount 6798
				}
				declare SendTraffic
				{
					uint64 BroadcastBytes 280189
					uint64 BroadcastCount 4041
					uint64 UnicastBytes 313403
					uint64 UnicastCount 6469
				}
			}
		}
	}
	declare VirtualLayer3SwitchList
	{
	}
}
Referencias
- Web de softether: https://www.softether.org/