Descripción
Se describe la arquitectura de Observabilidad securizada con
Keycloak. En primera instancia Grafana se configura para gestionar accesos usando OpenID. Por otro lado Grafana MIMIR y LOKI usarán OAuth2 con Authorization Code para web interfaces y OAuth2 con Client Credentials para APIs.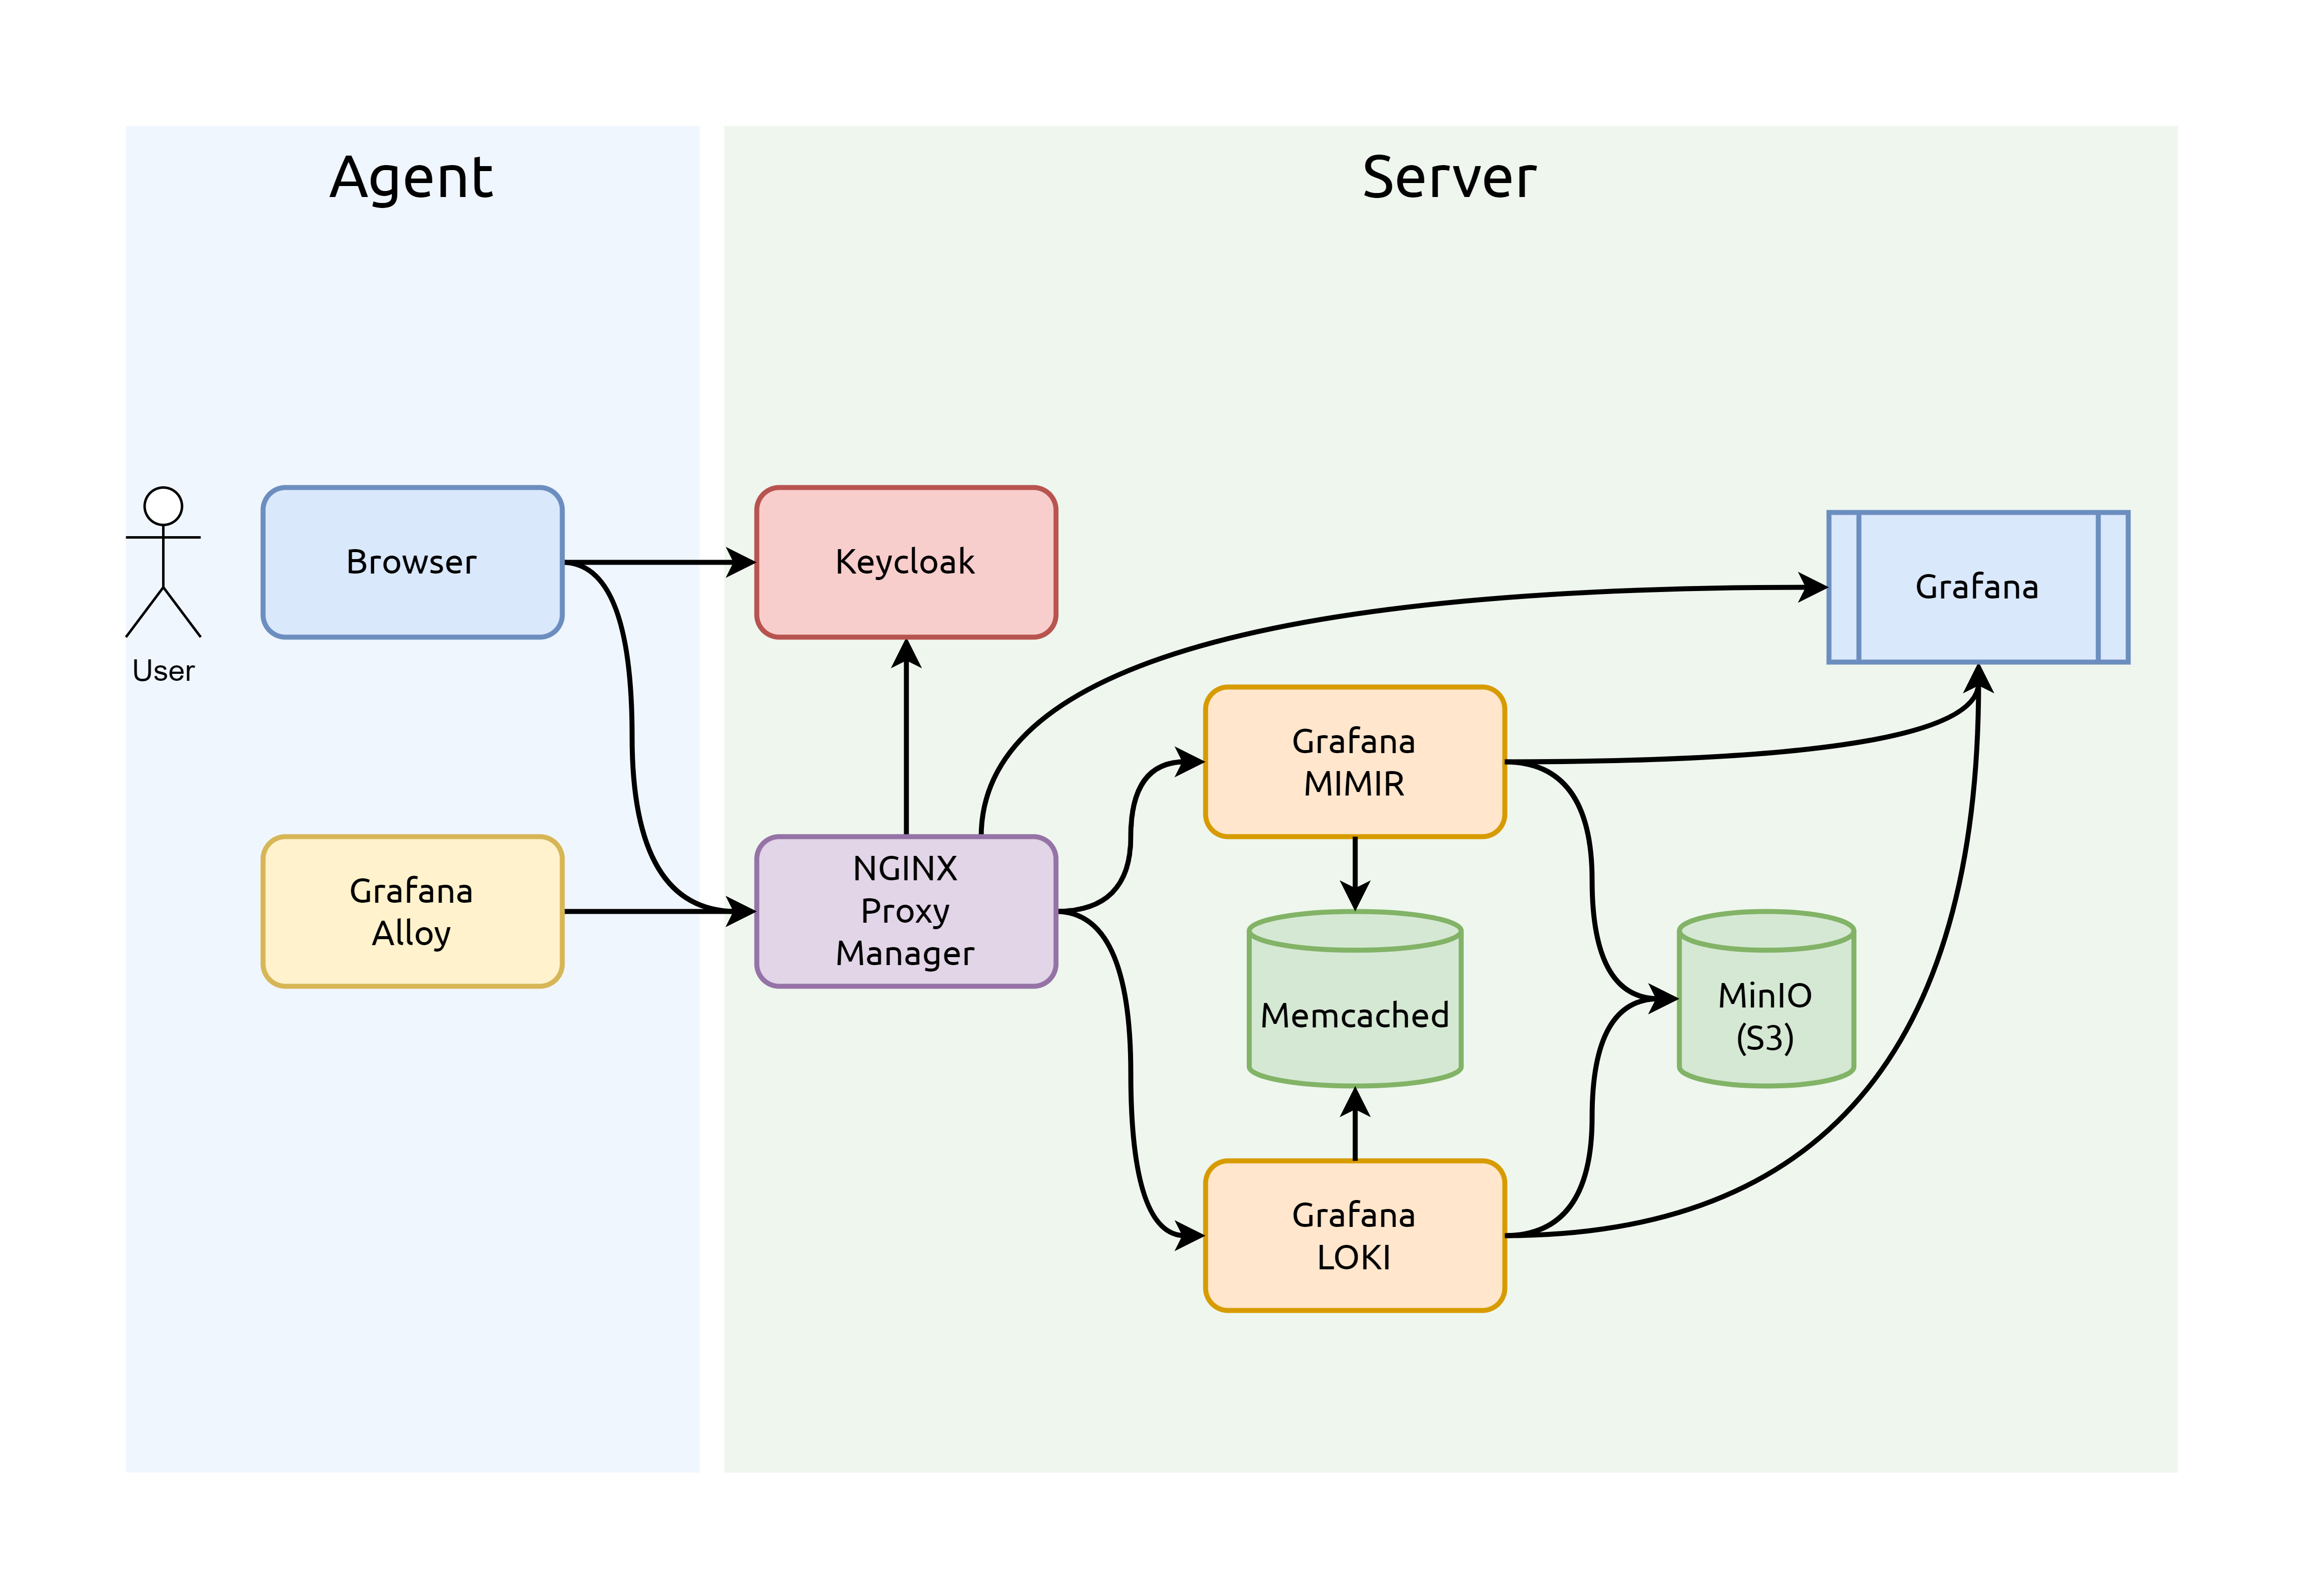
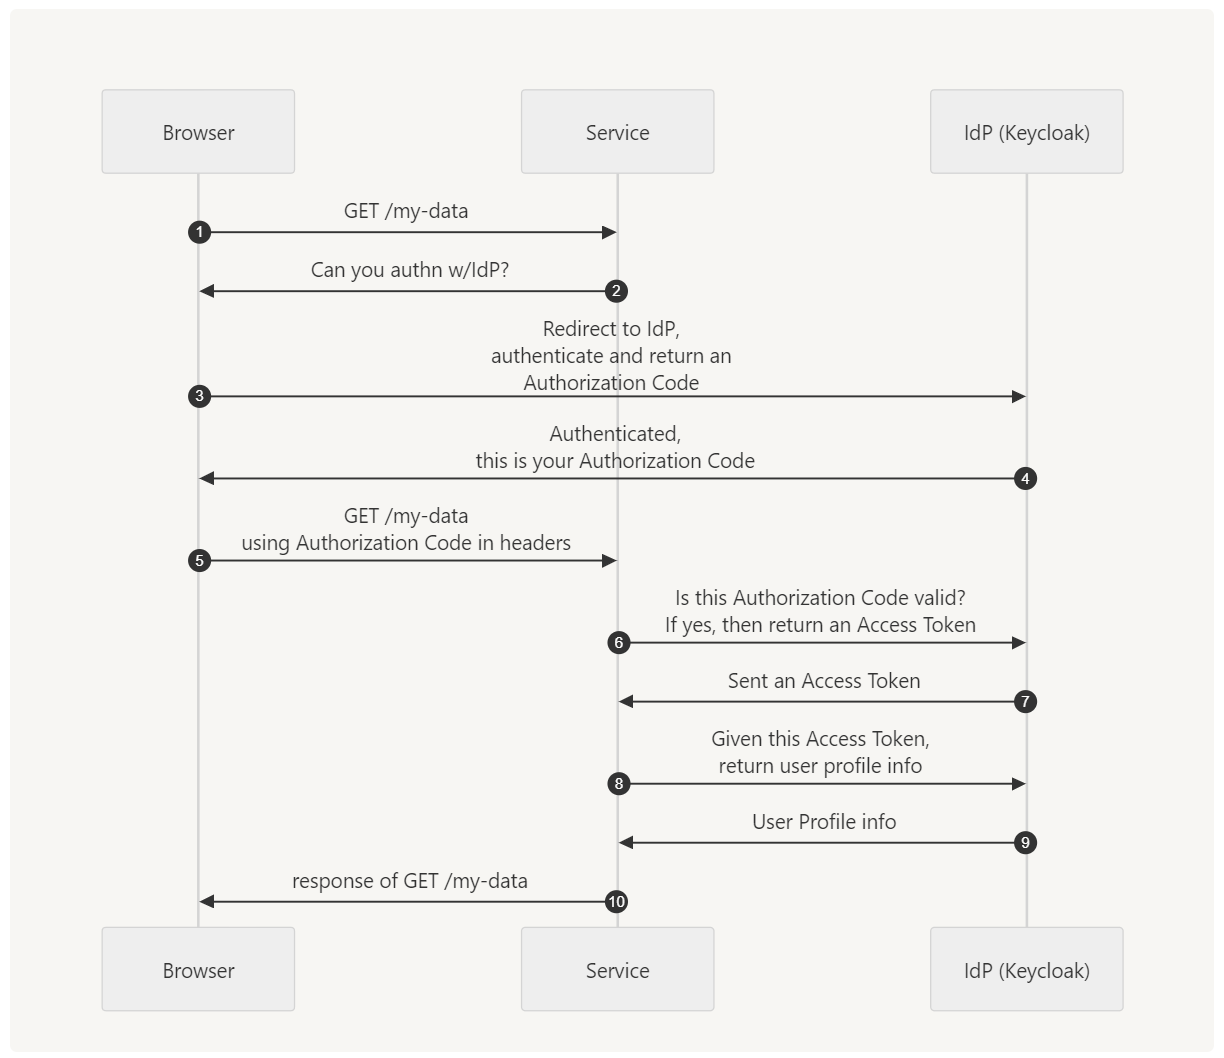
OAuth2 - Authorization Code (WUI)
original
sequenceDiagram
  autonumber
  participant Browser as Browser
  participant Server as Service
  participant IdP as IdP (Keycloak)
	Browser->>Server: GET /my-data
	Server->>Browser: Can you authn w/IdP?
	Browser->>IdP: Redirect to IdP,<br/> authenticate and return an<br/> Authorization Code
	IdP->>Browser: Authenticated,<br/>this is your Authorization Code
	Browser->>Server: GET /my-data<br/>using Authorization Code in headers
	Server->>IdP: Is this Authorization Code valid?<br/>If yes, then return an Access Token
	IdP->>Server: Sent an Access Token
	Server->>IdP: Given this Access Token,<br />return user profile info
	IdP->>Server: User Profile info
	Server->>Browser: response of GET /my-data
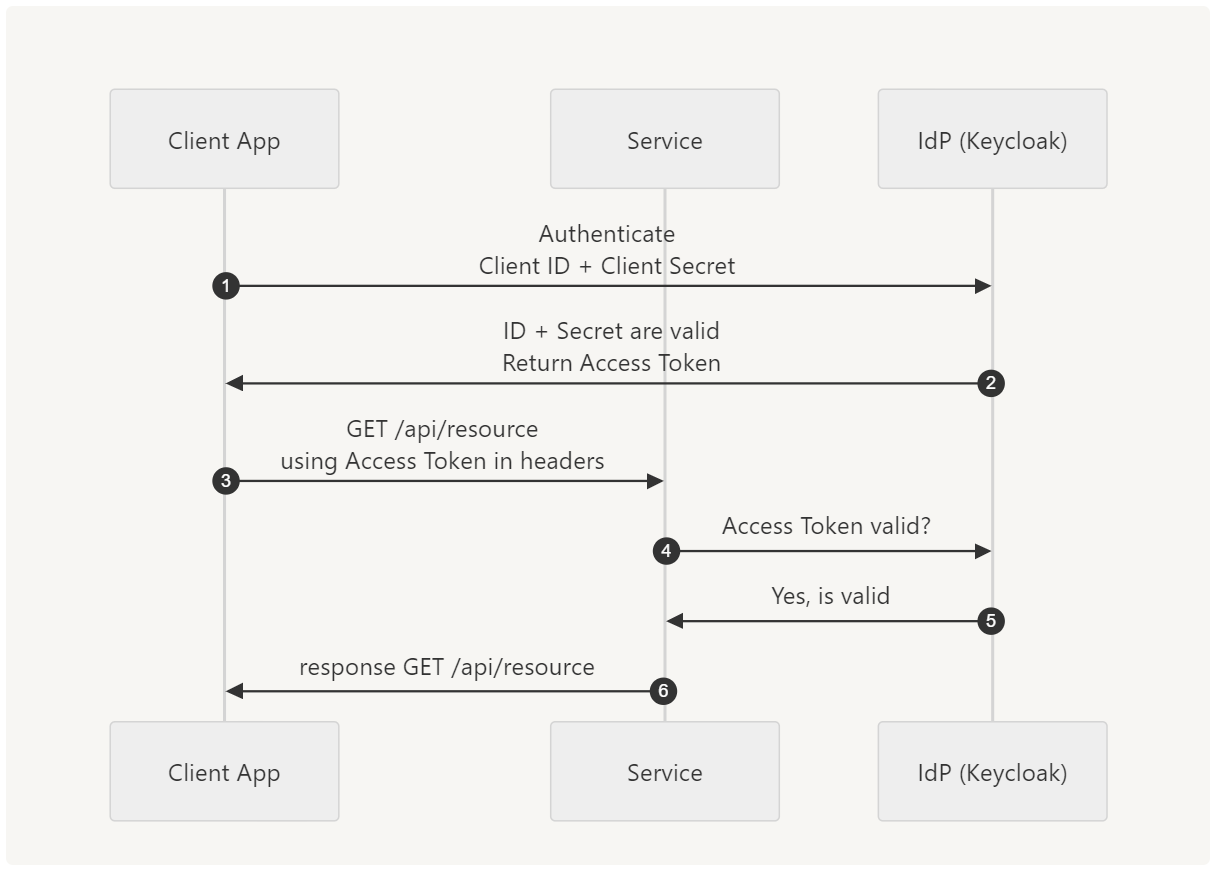
OAuth2 - Client Credentials (API)
original
sequenceDiagram
  autonumber
  participant ClientApp as Client App
  participant Server as Service
  participant IdP as IdP (Keycloak)
	ClientApp->>IdP: Authenticate<br />Client ID + Client Secret
	IdP->>ClientApp: ID + Secret are valid<br />Return Access Token
	ClientApp->>Server: GET /api/resource<br />using Access Token in headers
	Server->>IdP: Access Token valid?
	IdP->>Server: Yes, is valid
Server->>ClientApp: response GET /api/resource